讓 AI Agent、MCP Server、CLI 安全登入:從 PKCE 到 Gateway 的實作工作坊

讓 AI Agent、MCP Server、CLI 安全登入:OAuth 2.0、PKCE 與 MCP

2026 年 10 月 14 日,我在 Hello World Dev Conference 2026 帶了一場 90 分鐘的實作工作坊:「讓 AI Agent、MCP Server、CLI 安全登入」。這篇文章把工作坊的觀念與練習路線整理下來,讓沒到場的朋友也能從自己的筆電開始,走過一次 MCP 的授權流程。

當 Agent 能讀文件、查工單、寫入資料,接上工具只是開始。真正要回答的是:這次操作代表誰?可以做哪些事?這顆 Token 能用在哪個服務?出事後,要怎麼停止它的權限?

上一篇企業身分認證治理實戰談的是整體架構,這篇則把焦點拉近到一個 HTTP 請求:從沒有 Token 時的 401,一路追到登入、取得授權,以及 Server 決定接受或拒絕的那一刻。

[Read More]

誰能用、用多久、出事能不能即時關掉?——AI 工具爆發時代的企業身分認證治理實戰

演講封面:誰能用、用多久、出事能不能即時關掉?

整場分享以身分、授權期限與撤銷能力三個問題為主軸。(原投影片第 1 頁,可點圖放大。)

這次在 Hello World Dev Conference 2026,我分享了「誰能用、用多久、出事能不能即時關掉?——AI 工具爆發時代的企業身分認證治理實戰」。這篇文章把演講中的架構與導入思路整理下來,也補充幾個實作時必須分清楚的技術邊界。

過去兩年,當公司內部的 AI Agent、MCP Server、CLI 工具與自動化腳本越來越多,我們遇到的問題也跟著改變。工具能不能完成任務,已經只是第一關;接下來要回答的是:這個工具代表誰?可以存取哪些資源?授權什麼時候結束?如果憑證外洩,要在哪裡把它關掉?

如果每個新工具都自己接 LDAP、自己存 API Key、自己處理 Token,工具數量增加的同時,也是在增加一批沒有人能完整盤點的存取入口。這場分享,就是從這個現場出發。

[Read More]

MCP 2026-07-28 Specification Update Explained: Stateless Core, MRTR, Tasks, and Security Hardening

cover

MCP 2026-07-28 is not a minor release that merely renames fields. It moves the protocol core from “establish a bidirectional session, then exchange messages inside it” toward a model that better fits Web infrastructure: each request is self-describing, independently routable, and explicitly cacheable; interactions and long-running work have clear protocol contracts. This directly addresses common production problems: sticky routing, rolling deployments, gateways that cannot inspect bodies, retrying after disconnects, and OAuth trust boundaries.

This article draws on the official release announcement, changelog, specification, Go SDK v1.7.0, and nine executable examples in go-training/mcp-2026-07-28. Their roles differ: the specification defines wire semantics, the SDK defines the public Go API, and the examples and tests only demonstrate the behavior they cover. Tasks in particular are standardized in the specification, while v1.7.0 does not yet provide a complete typed API.

By the end, you should be able to answer four questions: how MCP becomes easier to scale horizontally, how to complete an interaction without a session, what a gateway can safely observe, and which layer server, client, and platform owners should migrate first.

For hands-on verification, refer to the training examples for 01 Stateless, 02 Subscriptions, 03 MRTR, 04 Cache, 05 HTTP headers, 06 Deprecations, 07 MCPGODEBUG, 08 Authorization, and 09 Extensions / Tasks.

AreaCommon 2025-11-25 model2026-07-28 focusPrimary beneficiary
ConnectionInitialization and a session bind subsequent trafficPer-request metadata and optional discoveryServer / platform
InteractionServer-initiated reverse RPCMRTR retries and the Tasks extensionClient / agent
ListingsRefetch or guess at cachingttlMs, cacheScope, and invalidationClient / LLM host
HTTPRouting requires parsing JSON bodiesMcp-* headers verified against the bodyGateway / SRE
ExtensibilityThe core keeps growingExplicit extensions with bilateral opt-inSDK / platform
[Read More]

MCP 2026-07-28 規格更新全解析:從無狀態核心、MRTR 到 Tasks 與安全強化

cover

MCP 2026-07-28 不是一次把欄位改名的小改版。它把協定核心從「先建立雙向 session,再在裡面交換訊息」改為更接近 Web 基礎設施擅長處理的模式:每個 request 自我描述、可獨立路由、可明確快取,互動與長工作則有明確的 protocol contract。這正好處理 production 最常見的麻煩:sticky routing、滾動部署、gateway 看不懂 body、斷線重試與 OAuth 信任邊界。

本文以官方 release announcement、changelog 與 specification、Go SDK v1.7.0,以及可執行的 go-training/mcp-2026-07-28 九組範例為依據。三者的角色不同:規格定義 wire semantics,SDK 定義公開 Go API,範例與測試只證明它實際覆蓋的行為;尤其 Tasks,規格已正式化,但 v1.7.0 尚未有完整 typed API。

讀完你應該能回答四件事:怎麼讓 MCP 更容易水平擴展、怎麼在無 session 下完成互動、gateway 能安全觀察什麼,以及 server、client、platform 各自該先遷移哪一層。

想邊讀邊驗證,可直接對照教材的 01 Stateless、02 Subscriptions、03 MRTR、04 Cache、05 HTTP headers、06 Deprecations、07 MCPGODEBUG、08 Authorization 與 09 Extensions / Tasks。

面向2025-11-25 常見模型2026-07-28 的重點主要受益者
連線initialization 與 session 綁住後續流量per-request metadata、optional discoveryserver/platform
互動server-initiated reverse RPCMRTR retry、Tasks extensionclient/agent
清單重抓或各自猜 cachettlMs、cacheScope、invalidationclient/LLM host
HTTProuting 要解析 JSON bodyMcp-* headers 並比對 bodygateway/SRE
擴充core 不斷長大雙方 opt-in extensionsSDK/platform
[Read More]

When AI Can Already Write Code — Building Your AI Workflow: Agent Skill + MCP Hands-on Workshop Recap

cover

On July 1, 2026, I ran a 90-minute hands-on LAB workshop at iThome Cloud Summit Taiwan: “When AI Can Already Write Code — Building Your AI Workflow”. This article walks through the core content and hands-on exercises from that day, so friends who couldn’t make it can follow along and run through it themselves, and attendees have a set of notes to come back to.

On the same day I also gave a conference talk about our complete two-year journey of adopting AI Agentic Coding — the recap is here: From Watching on the Sidelines to Company-Wide Adoption: Two Years of AI Agentic Coding in Practice. That talk covered the “why and how to drive adoption”; this LAB was about rolling up our sleeves and actually doing it.

[Read More]

當 AI 已經能寫 Code——打造你的 AI 工作流:Agent Skill + MCP 實戰工作坊回顧

cover

2026 年 7 月 1 日,我在 iThome 臺灣雲端大會(Cloud Summit Taiwan)帶了一場 90 分鐘的 LAB 實戰工作坊:「當 AI 已經能寫 code——打造你的 AI 工作流」。這篇文章整理當天的核心內容與動手練習,讓沒能到場的朋友也能照著跑一次,也給參加過的朋友一份可以回頭查的筆記。

同一天我還有一場議程演講,聊的是兩年 AI Agentic Coding 導入的完整歷程,回顧文在這裡:從觀望到全公司落地:兩年 AI Agentic Coding 導入實戰。那場講「為什麼與怎麼推」,這場 LAB 則是捲起袖子「實際動手做」。

[Read More]

From Watching on the Sidelines to Company-Wide Adoption: Two Years of AI Agentic Coding in Practice

cover

Date: 2026.07.01 Event: 2026 Cloud Summit Taiwan Speaker: appleboy

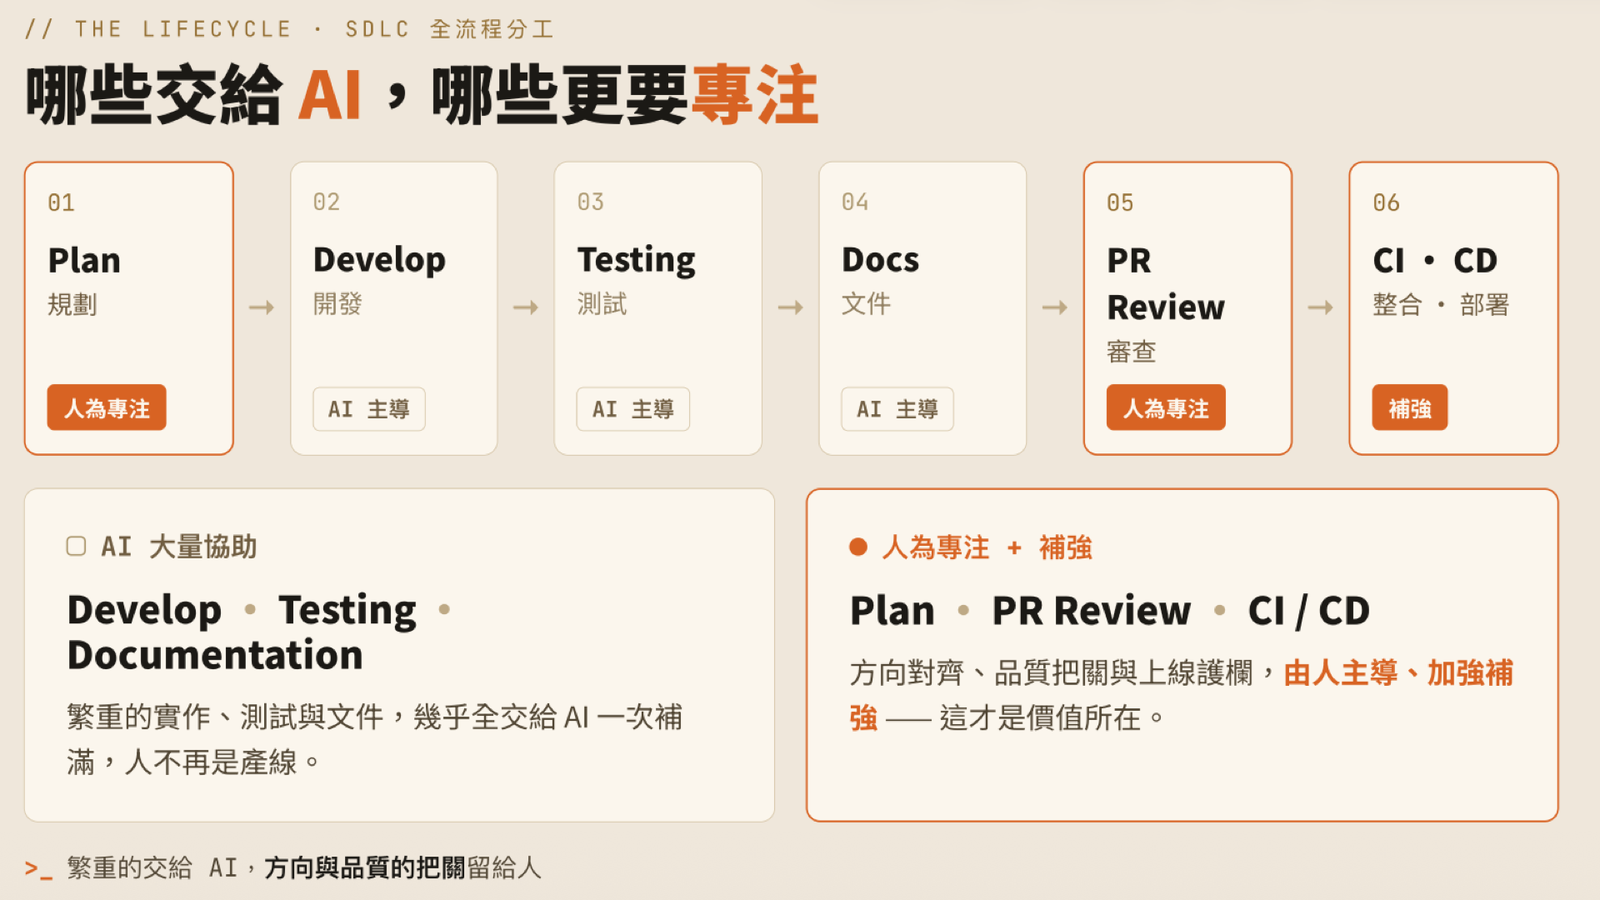
This time last year, the question we were asking was “how can AI help us improve our productivity?” This year, the question has flipped: “how can we help AI so that it accelerates our work?” Swapping the subject and the object sounds like wordplay, but it is exactly the most fundamental mindset shift we went through over these two years of rolling out AI Agentic Coding across the company.

This article documents a road we actually traveled: from a handful of people quietly trying out Claude Code, to everyone in the company using it daily; from AI producing 66% of our output, all the way up to 97%; from engineers’ three wait-and-see attitudes — “I don’t trust it, I’m afraid of being replaced, I’m worried about security” — to letting results speak for themselves and packaging individual tricks into standardized Agent Skills; from every team writing its own MCP Server and triggering a project explosion, to pulling the security governance of the whole ecosystem back together with a unified authentication gateway and a Marketplace review process.

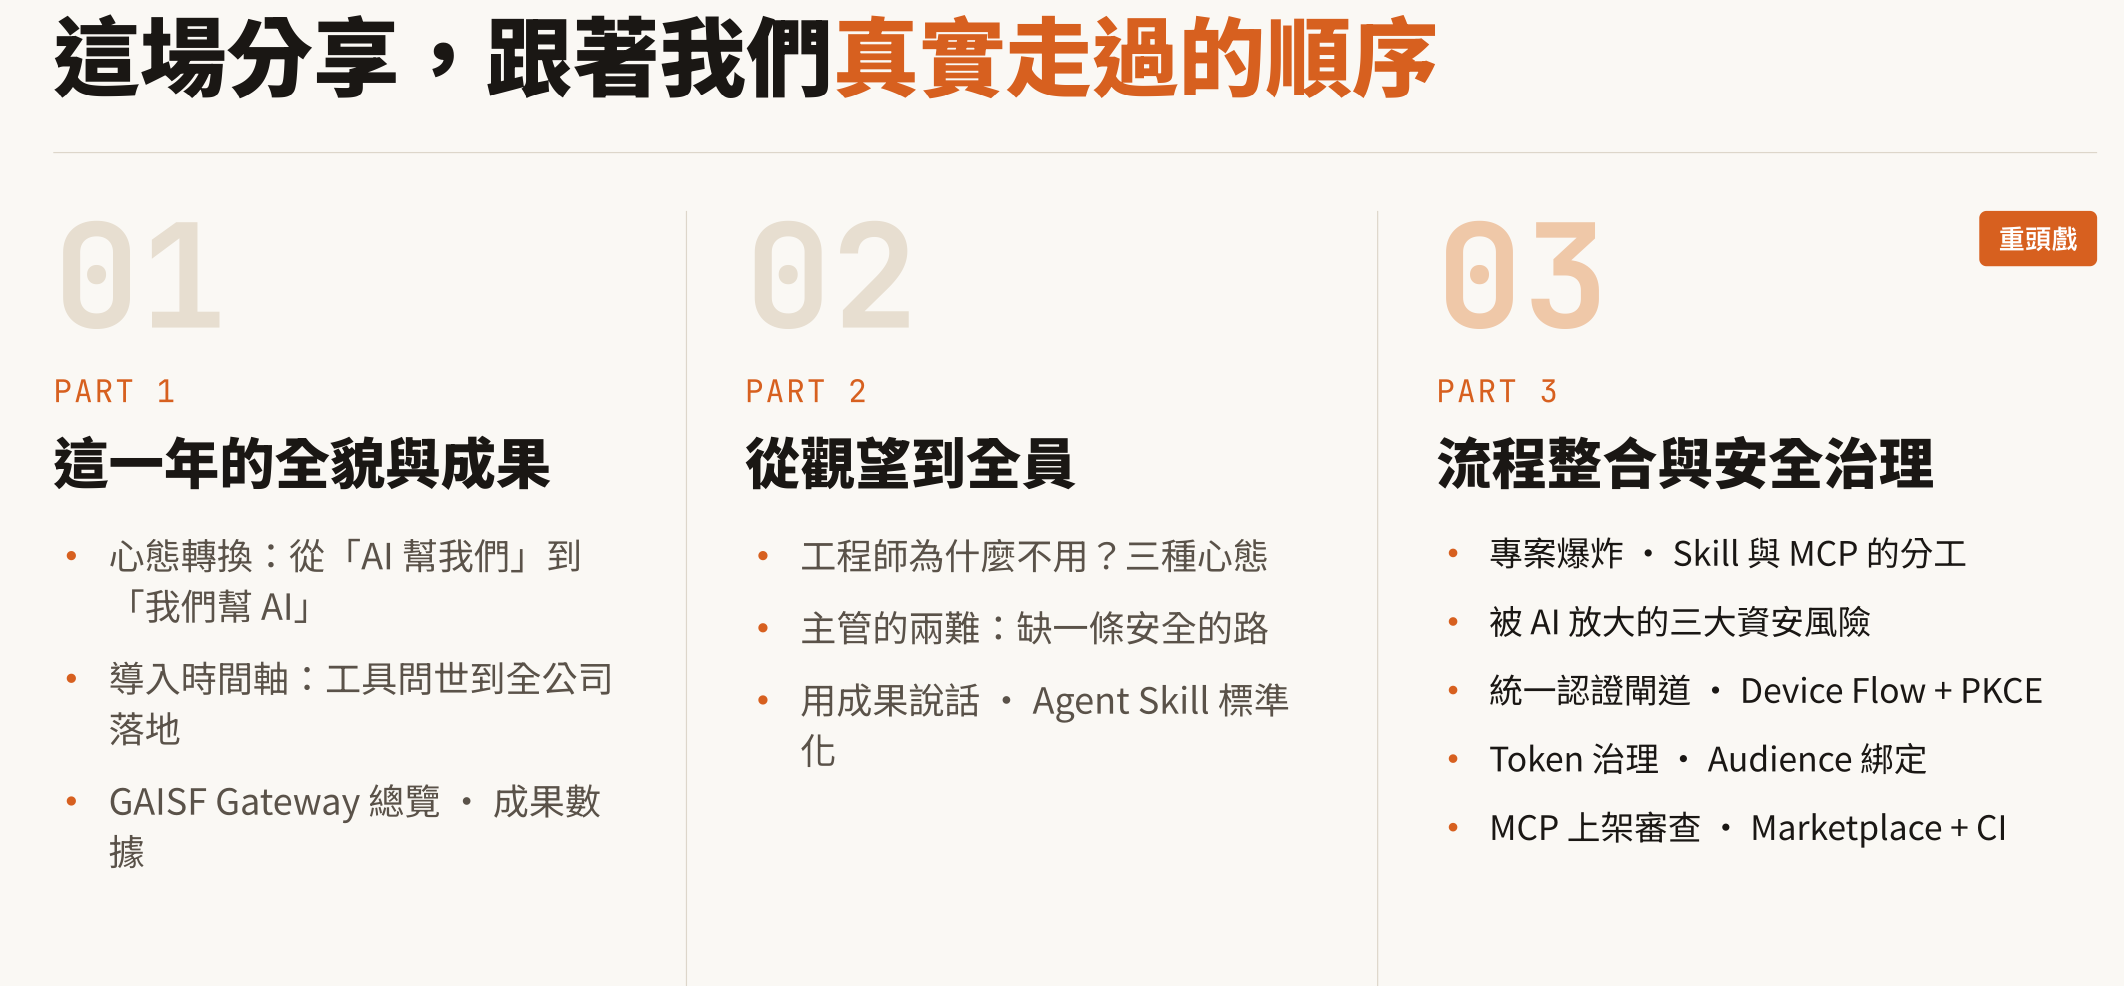
Three parts, in the order we actually lived through them: the full picture and the results of this year → from the sidelines to everyone on board → workflow integration and security governance.

[Read More]

從觀望到全公司落地:兩年 AI Agentic Coding 導入實戰

cover

日期:2026.07.01 活動:2026 Cloud Summit 台灣雲端大會 講者:appleboy

去年這個時候,我們在想的是「AI 怎麼協助我們改善工作效率」;今年,問題反過來了——「我們該怎麼協助 AI,讓它加速我們的工作」。主詞和受詞對調,聽起來像文字遊戲,但這正是這兩年公司內部 AI Agentic Coding 導入路上,最核心的一次心態轉變。

這篇文章記錄的是一段真實走過的路:從少數人偷偷試用 Claude Code,到全公司日常使用;從 AI 產出佔比 66%,一路衝到 97%;從工程師「不信任、怕被取代、擔心資安」的三種觀望心態,到用成果說話、把個人技巧封裝成標準化的 Agent Skill;從每個團隊各自寫 MCP Server 導致的專案爆炸,到用統一認證閘道與 Marketplace 審查機制把整個生態圈的資安治理收攏起來。

三個部分,跟著我們真實走過的順序:這一年的全貌與成果 → 從觀望到全員 → 流程整合與安全治理。

[Read More]

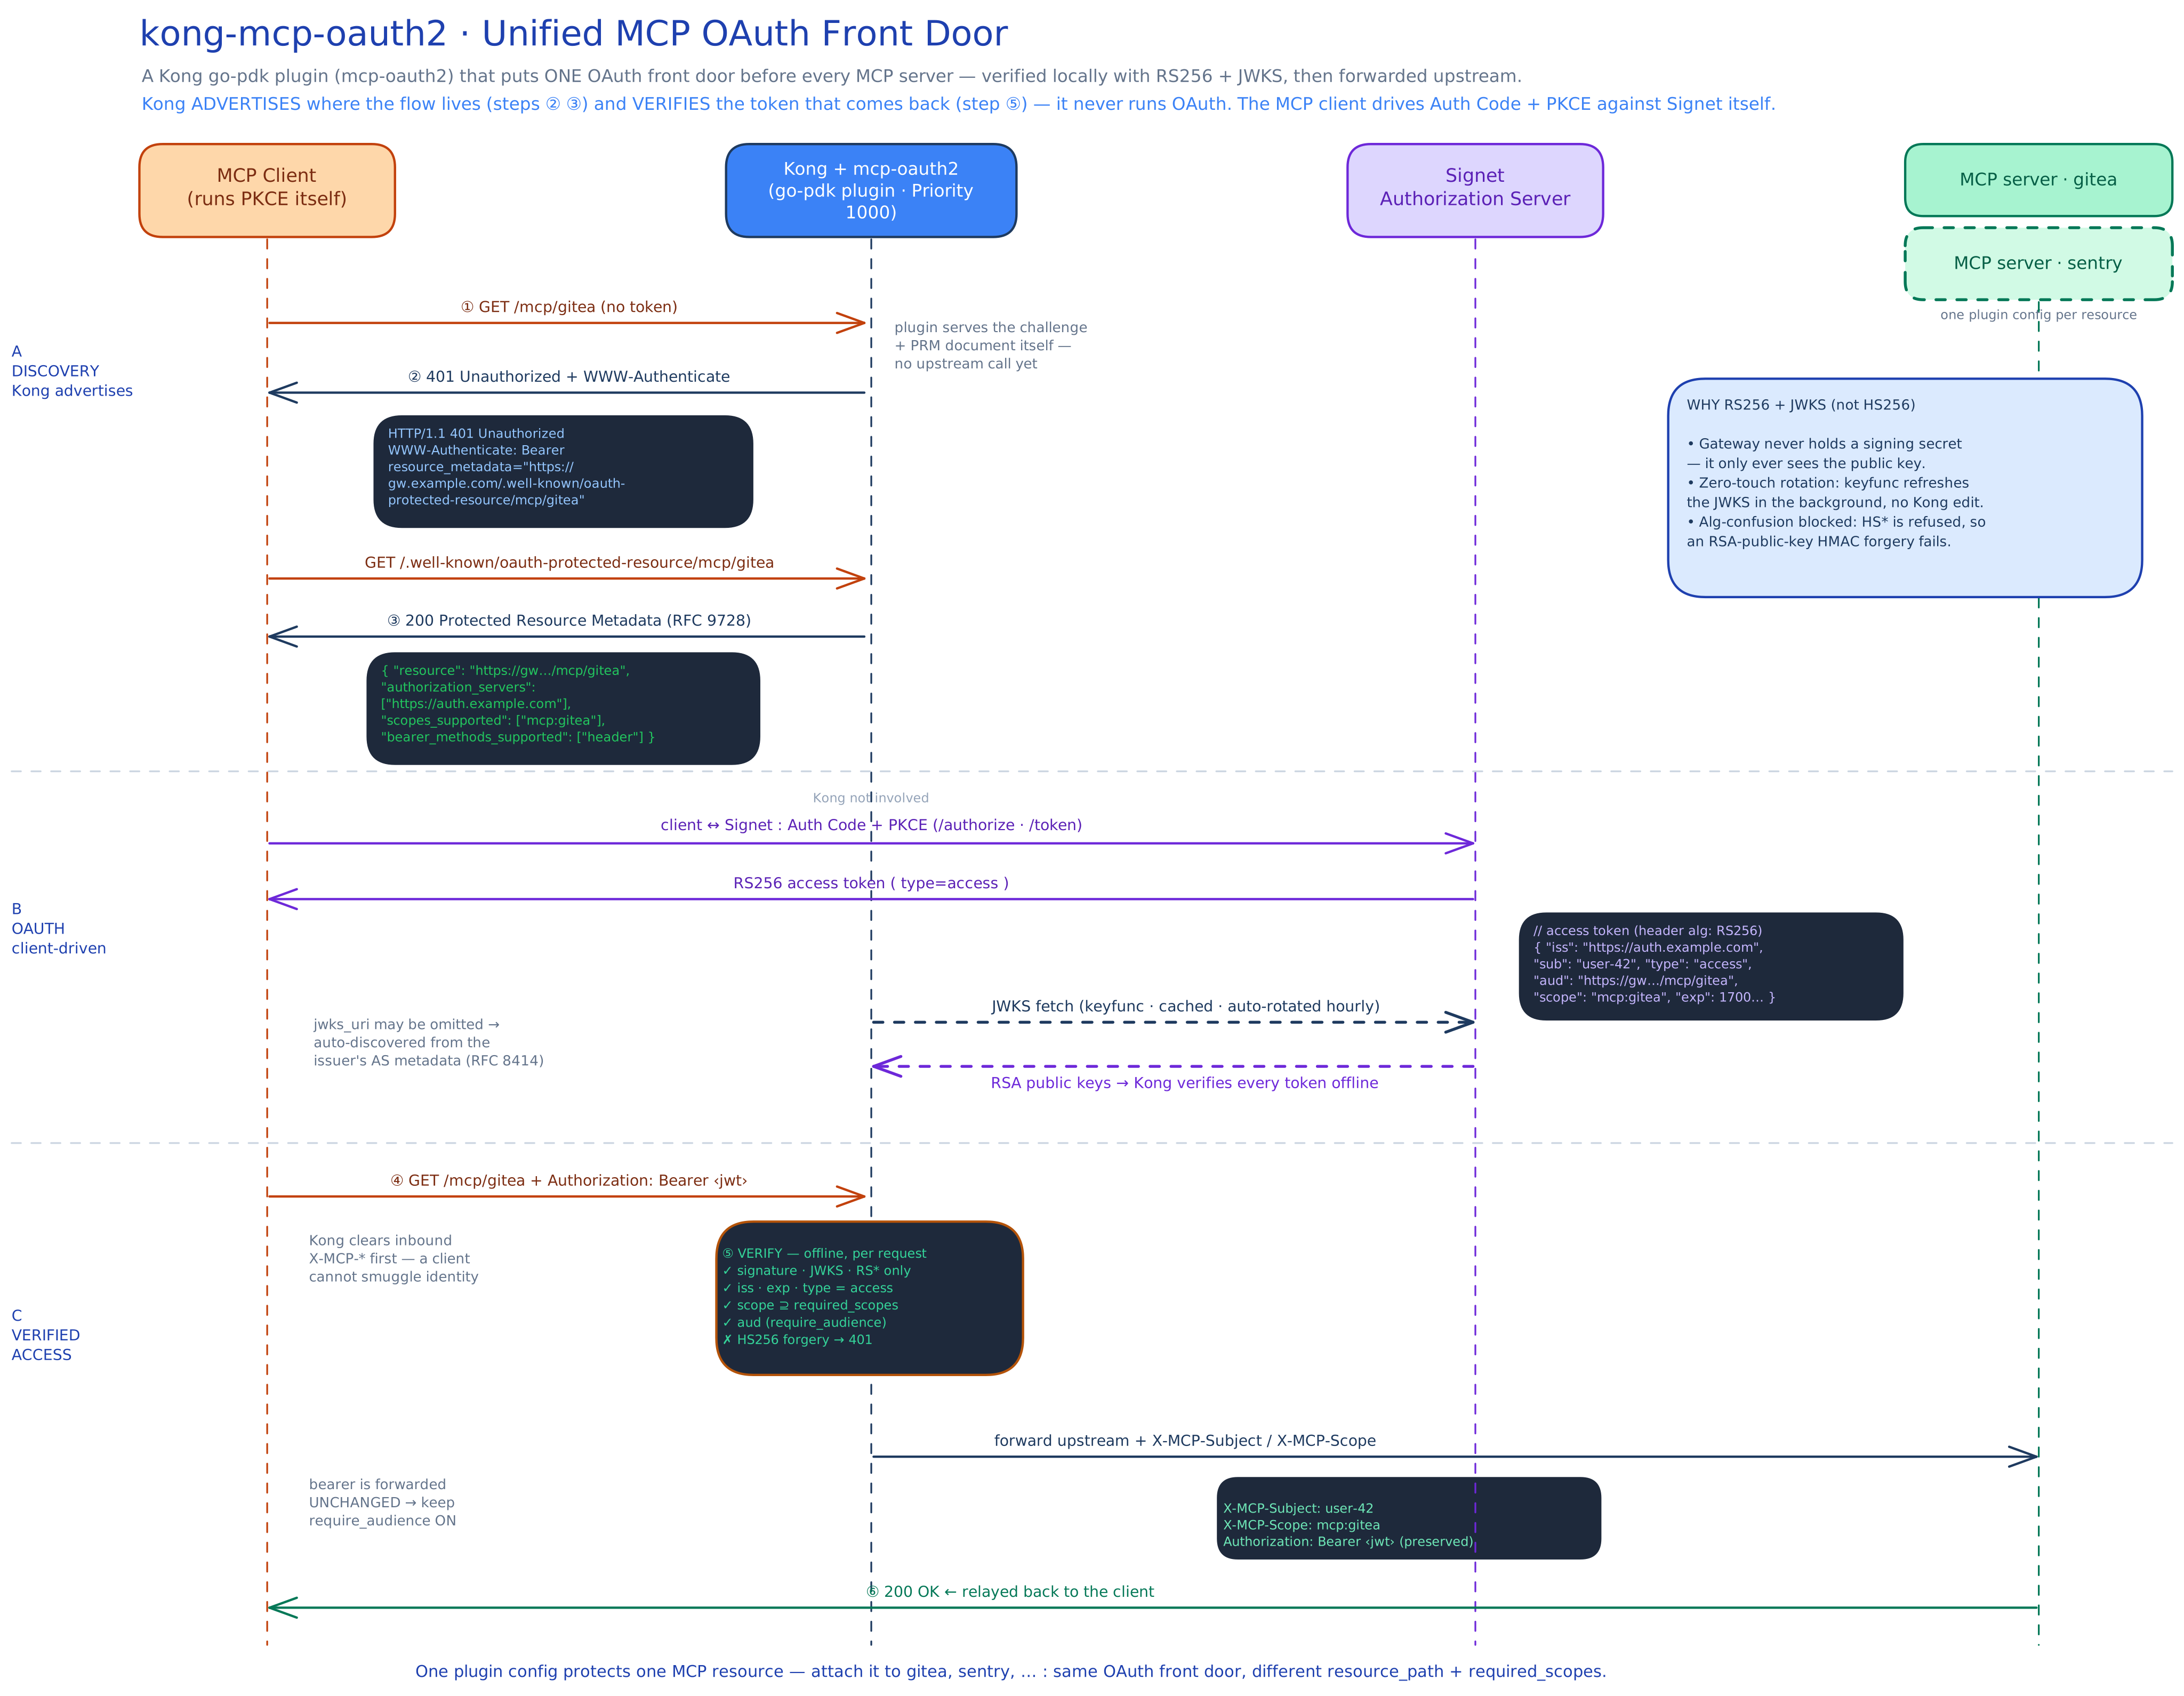
Stop Letting Every MCP Server Collect Its Own PAT: A Unified OAuth2 Front Door with Kong + Signet

cover

Once MCP (Model Context Protocol) exploded inside the company, almost every team ended up running an MCP server or two of their own: one fronting Gitea, one for Sentry, one for the internal Wiki, one for a database. They’re genuinely useful — but there’s a question everyone collectively ignored: how do these MCP servers actually authenticate?

The answer is usually unsettling: each one collects its own PAT (Personal Access Token). Every MCP server defines its own token, stuffs it into an environment variable, and validates it itself. So the company quietly accumulates a pile of static tokens — “long-lived, sitting in a file, equivalent to someone’s account” — scattered across dev machines, CI, even pasted into Slack messages. This post is about using Kong together with Signet to put a single OAuth2 front door in front of every MCP server and clean up that PAT sprawl in one move.

The full example code lives in appleboy/kong-mcp-oauth2. This post walks through the motivation, the architecture, the security considerations, and the actual verification steps.

[Read More]

別再讓 MCP Server 各自收 PAT:用 Kong + Signet 做企業統一 OAuth2 入口

cover

MCP(Model Context Protocol) 在公司內部爆量之後,幾乎每個團隊都自己跑了一兩個 MCP Server:接 Gitea 的、接 Sentry 的、接內部 Wiki 的、接資料庫的。它們很好用,但有一個被集體忽略的問題——這些 MCP Server 到底是怎麼認證的?

答案多半令人不安:各自收各自的 PAT(Personal Access Token)。每個 MCP Server 自己定義一套 token、自己塞進環境變數、自己驗。於是公司內部出現了一堆「長期有效、放在檔案裡、等同某個帳號權限」的靜態 token,散落在開發機、CI、甚至貼在 Slack 訊息裡。這篇文章要談的,就是怎麼用 Kong 搭配 Signet,在所有 MCP Server 前面架起單一的 OAuth2 入口,把這堆 PAT 一次收掉。

完整的範例程式碼在 appleboy/kong-mcp-oauth2,本文會帶你走過設計動機、架構、安全考量到實際驗證。

[Read More]